Harden an application
Review authentication, data handling and exposed interfaces, then address agreed weaknesses in the software.
Devtric solutions
Application and cloud hardening, authentication, permissions and audit logging for business software and infrastructure.
What we handle
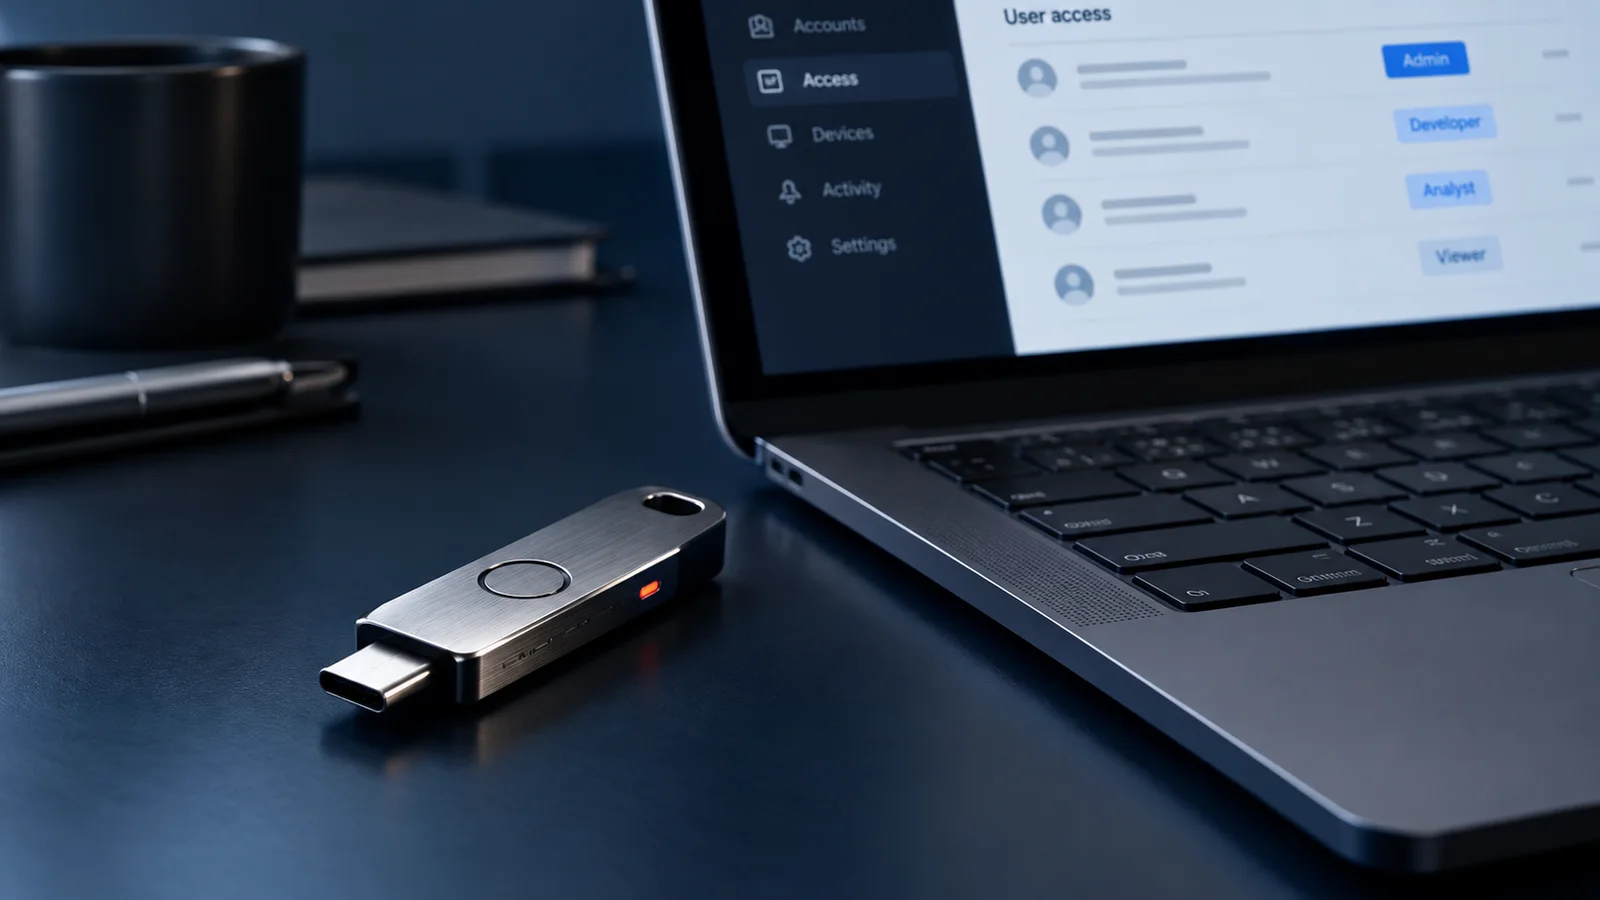
Security depends on everyday engineering decisions: who can sign in, what they can change, how sensitive data is handled and how issues are found and fixed. We review the agreed environment, prioritise practical improvements and implement changes within a defined scope.
Application security needs clear rules for who can sign in, what each role can do and which actions need a record. We review those controls alongside cloud configuration, system dependencies and the response to an alert.
Where it fits
Review authentication, data handling and exposed interfaces, then address agreed weaknesses in the software.
Give users and service accounts the permissions they need, with clear administration and audit records.
Review configuration, secrets, dependencies and deployment practices across the approved environment.
How we work
Agree the applications, cloud services, test boundaries and responsible system owners.
Inspect configuration and application controls, then agree the issues to address.
Apply the approved fixes and check the affected functionality and security controls.
Document changes, ownership, patching and the review practices needed after handover.
Delivery & handover
The final scope and acceptance criteria are agreed around your requirement.
Agreed system boundary and review scope
Findings and prioritised remediation plan
Implemented configuration or code changes
Verification of agreed fixes
Security configuration and operating documentation
The next step
Share what you have, what is getting in the way and what you need the system to do.